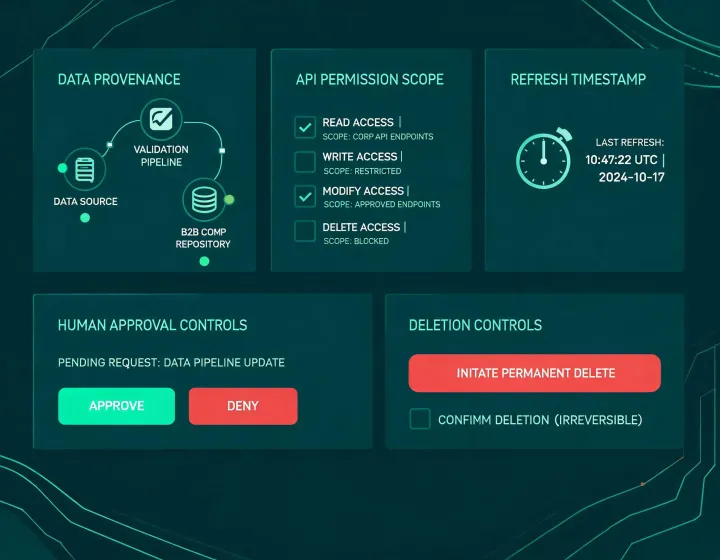
Data provenance
Record the provider, field, source date, permitted purpose, and fallback order. A waterfall can improve fill while making conflicts and deletion requests harder to explain.
Security & Data
Company intelligence is operationally trustworthy only when a reviewer can trace where a field came from, when it was observed, how it changed, and what the workflow may do next.
npx -y @okki-global/okki-go-taroballFact ledger
Record the provider, field, source date, permitted purpose, and fallback order. A waterfall can improve fill while making conflicts and deletion requests harder to explain.
Use environment secrets with minimum scope. Keep API keys out of prompts, repositories, shared screenshots, prospect exports, and error reports.
Review package permissions, outbound connections, retries, rate limits, logs, temporary files, and destinations. Installation success does not prove safe configuration.
Specify who can access intermediate and final records, how corrections propagate, when stale data expires, and how suppression or deletion is enforced.
Connection matrix
The labels below describe evaluation states, not official partnerships. Confirm supported runtimes and providers in current package documentation.
Evaluation method checked 21 July 2026. Changing vendor facts, pricing, certifications, and integrations must be confirmed from official sources.
| Dimension | Agent-native research | Seat-based platform | Reviewer test |
|---|---|---|---|
| Setup path | Package, runtime, configured sources | Managed application and account | Document every required permission |
| Task model | Natural-language brief with structured output | Saved filters and platform workflows | Run the same known cohort |
| Source disclosure | Depends on configured connector and output | Depends on vendor documentation | Demand field-level source and date |
| Human review | Must be designed as an explicit gate | Depends on team process | Trace who approved the next action |
| Security evidence | Inspect package and runtime locally | Review current vendor materials | Mark unconfirmed claims Unknown |
| Deletion control | Depends on every connected store | Depends on vendor and integrations | Test a correction and deletion end to end |
Unknown is a valid result. It is safer than turning absent public evidence into a favorable or unfavorable claim.
npx -y @okki-global/okki-go-taroballDo not connect live outreach until provenance, secret handling, access, retention, deletion, suppression, opt-out, and human approval controls have been tested.